PasteView.com
A secure, anonymous code and text sharing platform optimized for instant link generation. Scaled backend architecture to securely handle raw logs, configurations, and source code without account creation requirements.
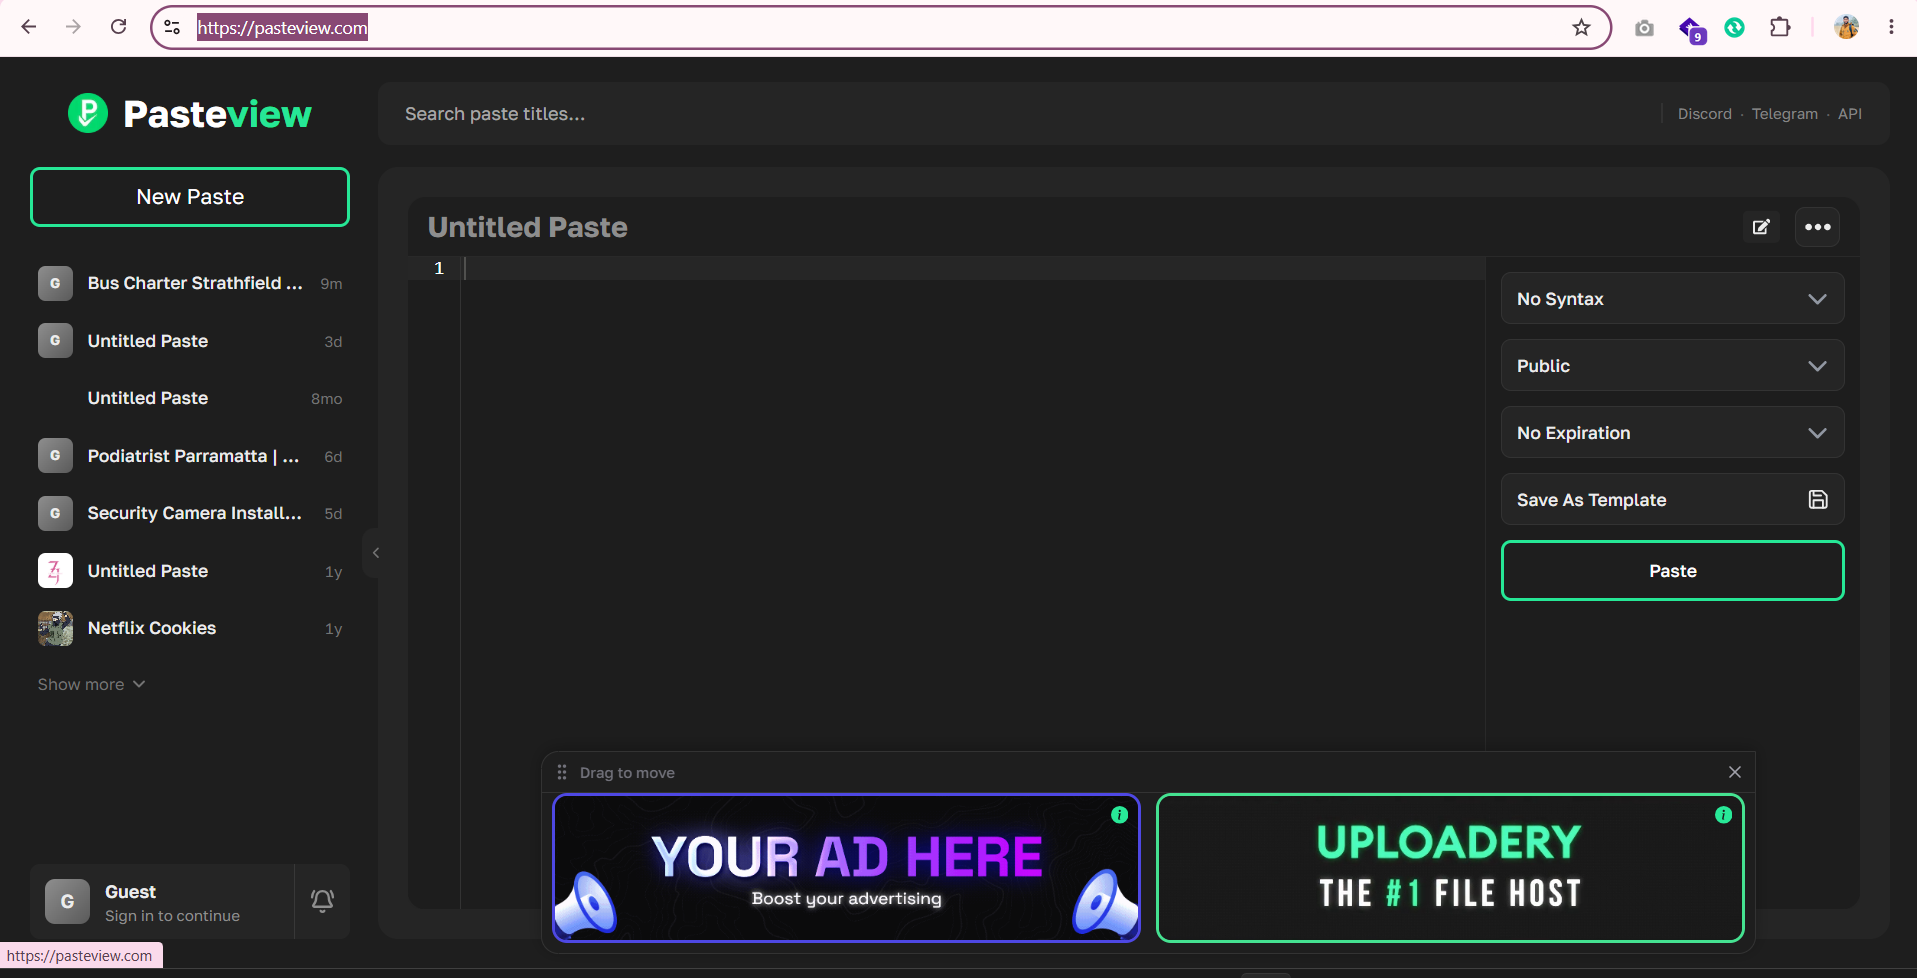
PasteView.com - High-Performance Text Sharing & Enterprise Security Hardening
Project Overview
PasteView is an anonymous text and source code sharing platform built for rapid, frictionless developer collaboration. The system allows users to immediately drop in raw content—ranging from multi-language source code snippets to 500+ line infrastructure log files—and instantly generate a shareable URL without forcing account creation or onboarding flows.
To support this zero-friction utility safely, this initiative focused on comprehensive backend security hardening and engineering defensive mitigation layers. The codebase underwent an exhaustive transformation to eliminate common public-facing data sharing vulnerabilities while keeping the core workflow fast, simple, and high-performance.
Key Features
⚡ Frictionless Paste Sharing Engine
- Accountless Instant Generation: Streamlined utility workflow allowing users to paste plain text, error logs, or configs and generate a direct shareable URL in under three steps.
- Multi-Format Storage Capabilities: Optimized text ingestion designed to seamlessly hold massive text payloads, structural configuration formats, and multi-language source code arrays (Python, JavaScript, C++, etc.).
- Optimized High-Volume Viewers: Lightweight, scannable reader interfaces built to instantly render distributed links across communication platforms like Discord or WhatsApp without browser layout shift.
🔐 Advanced Security Overhaul & Hardening
- IDOR & Parameter Isolation: Eradicated Insecure Direct Object References by completely restructuring runtime link parameters and ensuring strict read/write document ownership checks.
- Injection & Middleware Protection: Hardened MongoDB queries against NoSQL injection risks using object schema validation and strict parameter sanitation. Integrated security protection headers via Helmet.js.
- Anti-Abuse Routing & Rate Limiting: Implemented specialized window-based rate limiters to shield public paste creation endpoints against raw automated generation bots and volumetric brute-force flooding.
🧪 Automated Quality & Verification Engine
- 158 Backend Integration Tests: Programmed an extensive validation suite covering access parameters, query injection boundaries, and rate limit ceilings.
- Regression Protection: Established zero-regression guarantees ensuring that future updates to storage handlers or formatting styles cannot re-introduce security vulnerabilities.
Technical Stack
Backend Engine: Node.js, Express.js
Database: MongoDB, Mongoose ORM
Security Layers: Helmet.js, express-rate-limit, CORS Middleware, Data Sanitization Filters
Testing Automation: Jest, Supertest
Business Impact
- ✅ Zero-Friction Access Maintained: Preserved the platform’s core competitive value (instant sharing without accounts) while locking down back-end exploit routes.
- ✅ 158 Integrity Safeguards: Complete codebase verification covering every single public route variant to prevent performance or vulnerability regression.
- ✅ Enterprise Security Standard: Completely mitigated high-risk text-hosting vectors (NoSQL injections, Mass Assignment, IDOR) to ensure safe, scalable, and lightweight user operations.